Embed the following code in the head TAB of the business-critical entry page
<script type="text/javascript">
	(function(){
		window._fmOpt = {
			success: function(data) {
				console.log('blackBox: ', data)
			}
		};
		var fm = document.createElement('script');
                fm.type = 'text/javascript'; fm.async = true;
		fm.src = 'Base URL' + '?t=' + (new Date().getTime()/3600000).toFixed(0);
		var s = document.getElementsByTagName('script')[0];
                s.parentNode.insertBefore(fm, s);
	})();
</script>1.Create Base URL
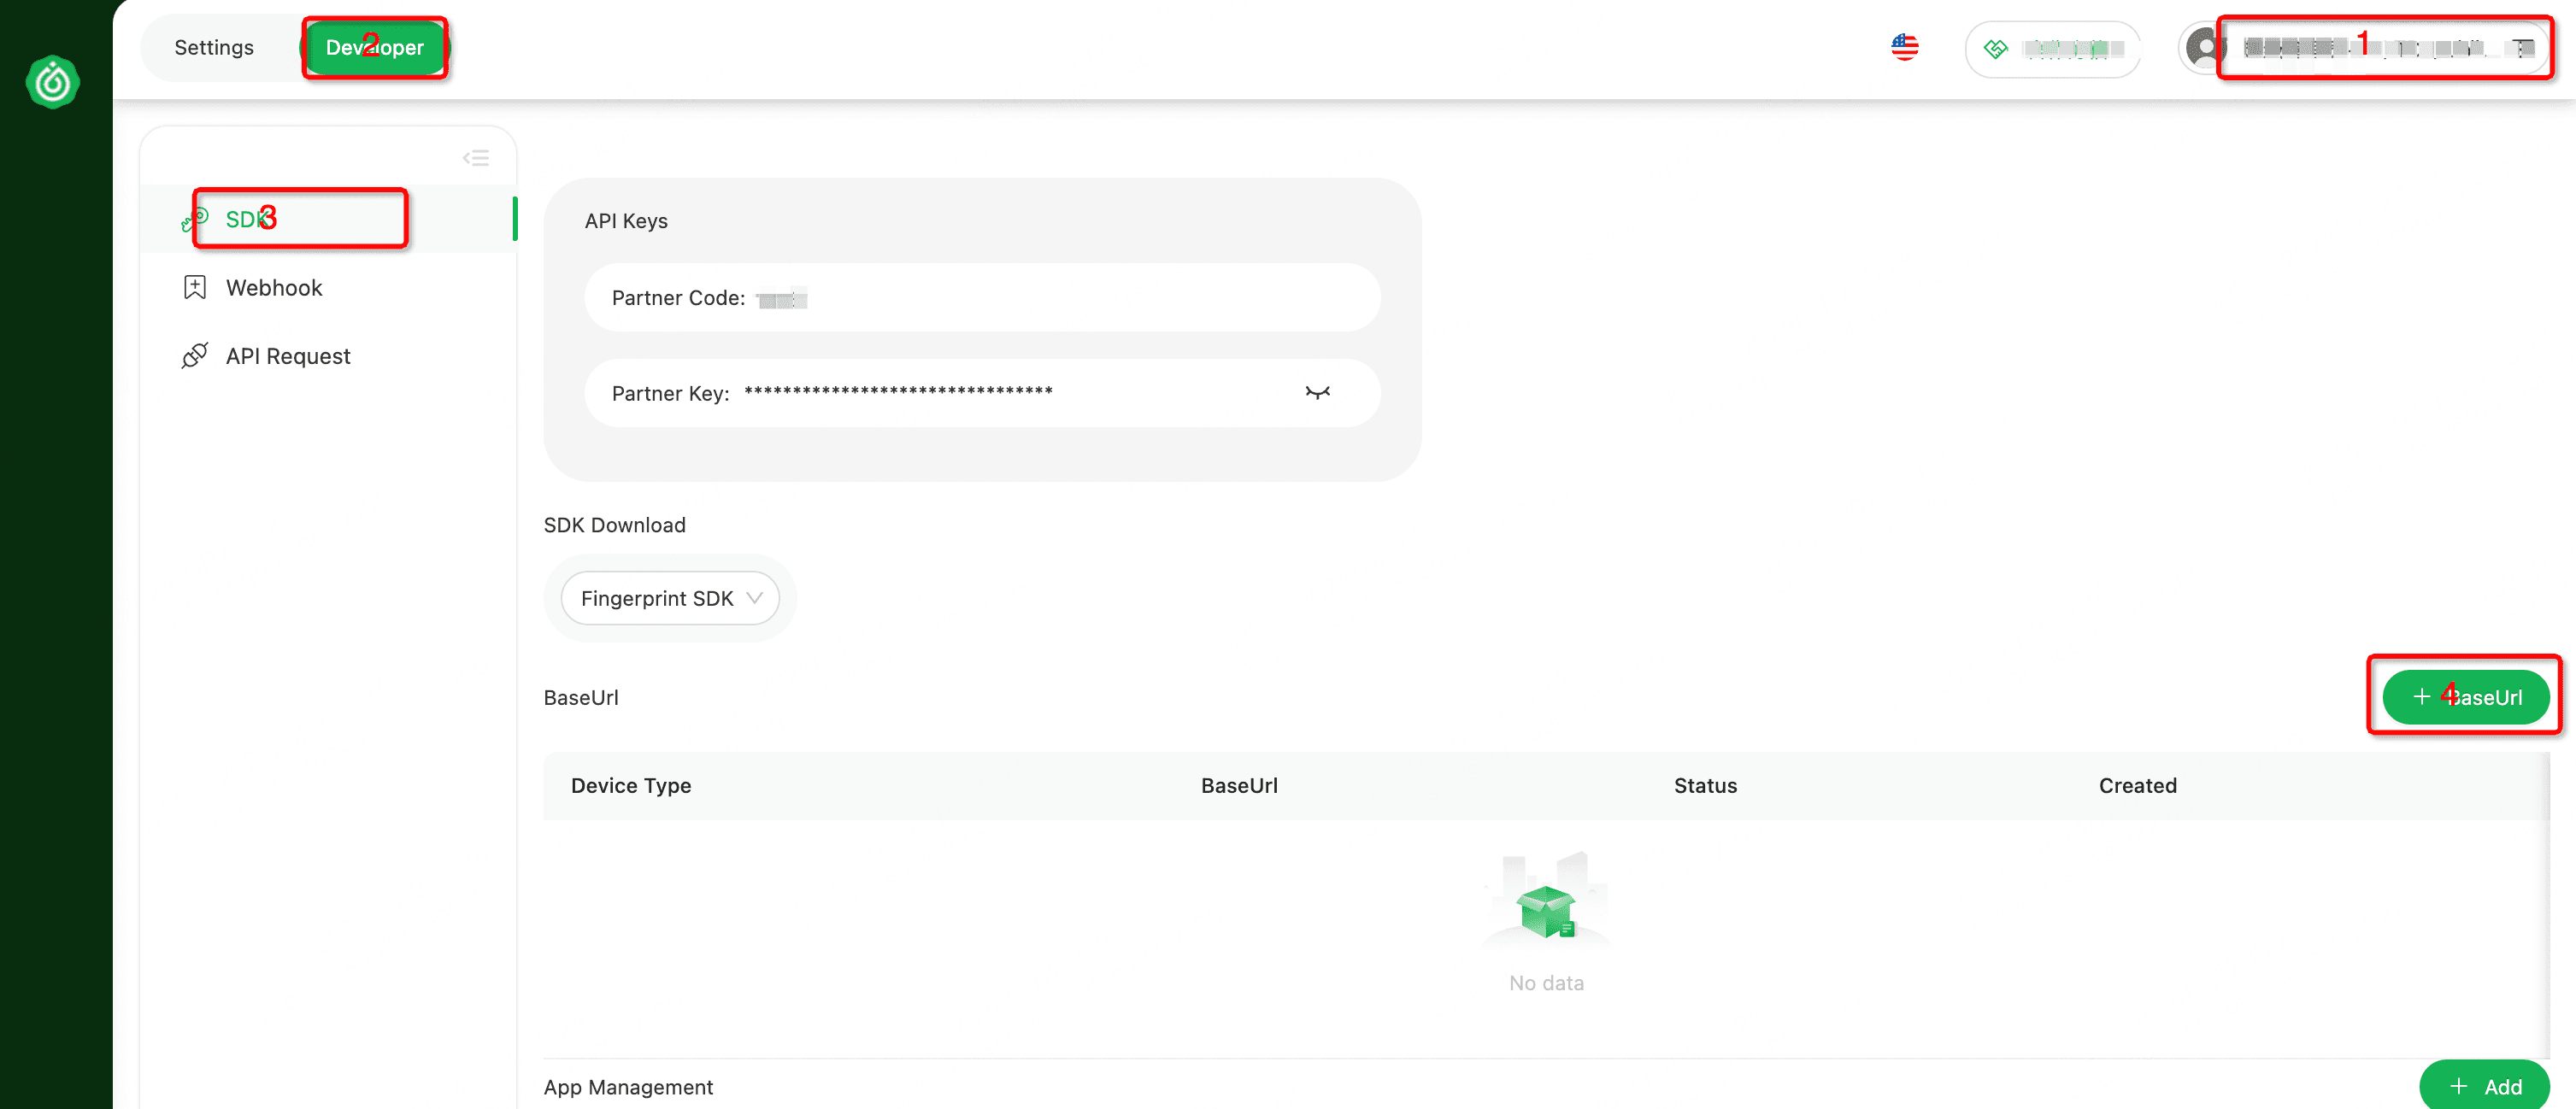
2.Copy Base URL

if (navigator.geolocation) {
  // The first execution will trigger the pop-up box for authorization
  navigator.geolocation.getCurrentPosition(function () {}, function () {});
} else {
  // The current environment does not support obtaining geographical location information
}The synchronous method may increase the probability of generating a degraded "blackBox". Please use it with caution in combination with the business scenario.
if (window._fmOpt && window._fmOpt.getinfo) {
  // Synchronously obtain the blackBox
  var your_blackBox = window._fmOpt.getinfo()
} else {
  // JSSDK has not been loaded completely
}If your page or gateway has configured content security policy (CSP) security restrictions, which limit scripts, workers, images, and interface domains.
please configure it in the CSP:
Content-Security-Policy: script-src 'self' 'wasm-unsafe-eval' 'unsafe-inline' https://*.trustdecision.com; worker-src 'self' blob:;img-src 'self' data:; connect-src 'self' https://*.apitd.netObtain by source code file
/**
 * TrustDeviceJs Pro v4.2.7 - Copyright (c) TrustDeviceJs, Inc, 2026 (https://www.trustdecision.com/solutions/trustdevice)
*/
Obtain by code in runtime
window._fmOpt.sdkVersion